
2024.08.08. The Fair Economy — AhnLab (CEO Kang Seok-gyun) announced on the 7th that it had recently discovered phishing emails exploiting the summer vacation season, impersonating corporate HR departments with false messages about changes to paid leave in an attempt to steal corporate email account credentials.
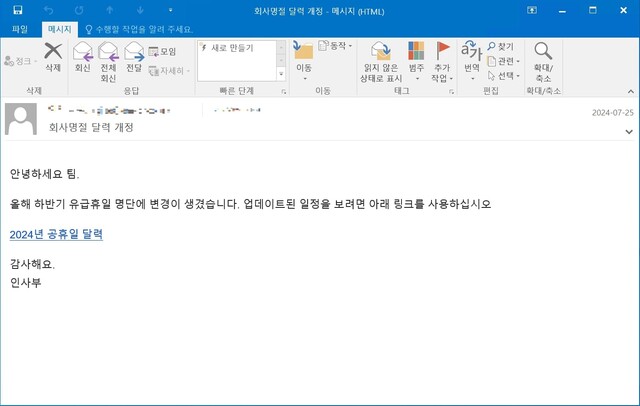
According to AhnLab, the attacker first impersonated the corporate HR department and distributed a phishing email titled "Company Holiday Calendar Revision".
The body of the phishing email stated, "There have been changes to the paid holiday list for the second half of this year, so click the link below to check the updated schedule," inducing recipients to click a malicious link. The link was inserted under the name "2024 Public Holiday Calendar."
When a deceived user clicks the link, a login page appears prompting them to enter their corporate email account information. Any password entered on that page is immediately sent to the attacker.
Given that the attackers impersonated a specific company's HR department to send the phishing email and that the user's email address was pre-filled in the fake login window, it is presumed that the attackers prepared the attack in advance, such as by collecting the email addresses of employees at the targeted organization. Since attackers can use the stolen account information to carry out further attacks impersonating company personnel, users need to exercise particular caution.
AhnLab's V3 currently supports detection and execution blocking for the malicious URL being distributed via this email, and AhnLab MDS, a sandbox-based advanced persistent threat (APT) response solution, is blocking the email in question.
In addition, AhnLab provides professional, up-to-date threat information related to phishing email attacks, including indicators of compromise (IoC), through its next-generation threat intelligence platform, AhnLab TIP.
To prevent damage from phishing emails, users should follow basic security practices, including checking the sender of emails and refraining from opening attachments or URLs from suspicious messages; using different accounts for different sites and periodically changing passwords; keeping antivirus programs such as V3 up to date and enabling phishing site blocking; and maintaining the latest versions of software in use (OS, web browser, office applications, etc.) and applying security patches.
Lee Ik-gyu, a researcher on AhnLab's analysis team, emphasized, "As in this case, phishing emails using keywords that are likely to tempt users, such as 'paid leave' and 'public holidays,' are discovered every year during vacation season." He added, "Users should carefully check the email address even from a familiar-looking sender, and organizations should block phishing email attacks targeting employees with appropriate security solutions and services."


0 Comments
No comments yet.