
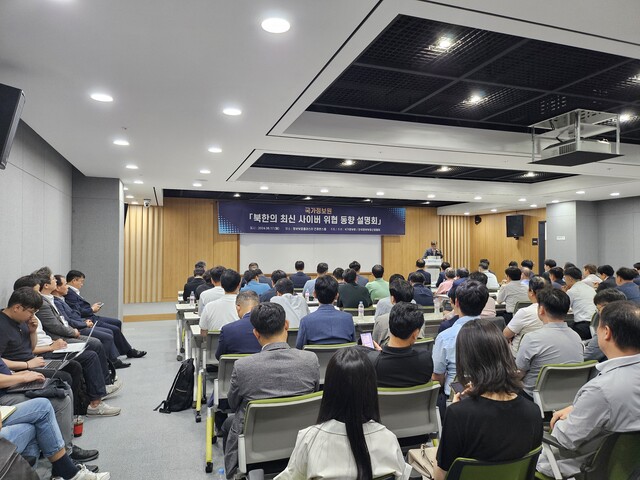
2024.06.18. The Fair Economy — The National Intelligence Service (NIS) announced on the 17th that it held a briefing session titled 'Analysis of North Korean Cyber Threat Trends and Attack Cases' at the Pangyo Corporate Support Hub, inviting officials from information security companies affiliated with the Korea Information Security Industry Association (KISIA).
The NIS explained the trend of increasing North Korean hacking attacks targeting domestic security products, as well as cases of new software supply chain attacks in which attackers infiltrate security companies' servers, steal source code, and then discover and exploit vulnerabilities. It also provided guidance on preventive measures and response procedures for security incidents, and on managing certified products.
In particular, the NIS disclosed more advanced software supply chain attack methods, such as not directly attacking target organizations but stealthily attacking developers or update servers to widely distribute malware. It urged the information security industry to actively cooperate in strengthening not only the safety of security products but also software supply chain security.
The Director of the National Cyber Security Center said, "As North Korea's cyber attack techniques grow increasingly intelligent and sophisticated day by day, software supply chain attacks targeting not only private companies but also state institutions and critical infrastructure are expanding." He added, "It is vital that security firms, which guard the first line of defense in cybersecurity, develop and distribute excellent security solutions."
Cho Yeong-cheol, chairman of KISIA, expressed gratitude, saying, "It is unusual for the NIS to directly hold a briefing session for information security companies. The latest North Korean attack techniques explained by the NIS will be of great help to companies in developing safer products."
Officials from the information security industry who attended the briefing said, "This served as an opportunity to once again realize that no matter how competitive a company's products are, it cannot survive and grow without security as a precondition." They added that they would actively cooperate to ensure follow-up measures, such as the swift development of emergency security patches in the event of a hacking incident, are carried out promptly.


0 Comments
No comments yet.